
"Putting customer data in Claude — is that safe?"
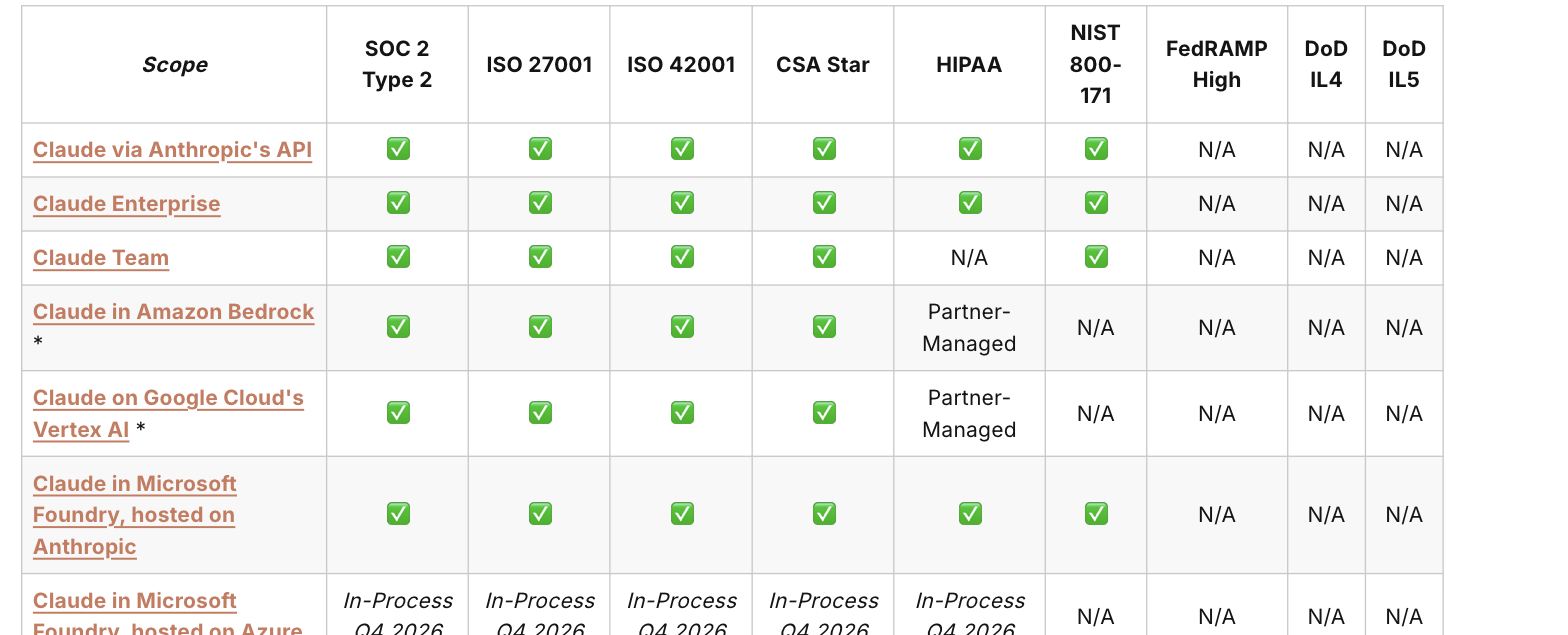
Most of the time, when a business won't approve Claude or some other AI tool, they call it "risk."
I think they mean 80% procurement friction, 20% risk.
Here's what I mean.
Microsoft shop? They reach for Copilot. Google shop? Gemini. Not because they ran a bake-off and those tools won on safety — but because the cat's already out of the bag. The paper's signed. The DPA, the security review, the SSO and SCIM config. Done. They sleep fine with those tools inside the tenant.
What they're actually saying is: "I don't want another vendor relationship." Another DPA. Another procurement cycle. Another afternoon wiring up SSO.
They're not saying they trust Microsoft more than they trust Anthropic.
Here's what gets me, though.
Businesses rip out and replace core systems all the time. Accounting platforms. CRMs. I can't remember the last time I heard someone on HubSpot say, "I don't know if we can move to Salesforce — it's too risky." They call it a project. They scope it, they staff it, they do it.
But adding AI to the same stack? Suddenly it's "risk." Suddenly it's a philosophical debate instead of a Tuesday.
Somehow, the most consequential tooling shift in a generation got filed under "scary" — when the honest label is "paperwork."
And I'm here to call it out for what it is.
"But it's a new attack surface." Yeah. It is.
So is every SaaS tool you've ever bought. And you already know how to fence one in — SSO, DLP, scoped data access, audit logs, a signed DPA, and a toggle to turn off training on your data. This isn't a new security paradigm you have to invent. It's the one you already run, pointed at one more vendor.
And here's the part that should reframe the whole debate.
Every real AI horror story I hear — actual dollars lost, actual lawsuits — traces back to a human doing something careless. Not a vendor breach. Not a missing DPA.
A lawyer who filed a brief full of cases the AI invented, without reading it. Air Canada's chatbot confidently promising a refund policy that didn't exist — and a tribunal making them pay it.
No procurement gauntlet on earth prevents that. The risk that actually bites isn't the vendor you onboarded. It's whether a human looked at the output.
So be honest about which conversation you're actually in.
Sometimes the honest answer is "not worth it" — and that's a fine call. You don't switch banks because the one down the street pays 1% more interest. It's just as reputable, the rate's better, but re-pointing every recurring transaction is a lot of friction for a little upside.
But 0.5% versus 7%? Now you move. The friction's the same; the payoff isn't.
So be honest about the delta, too. If the better tool for the job is the one you haven't papered yet, the real work isn't a security debate about Microsoft vs. Anthropic. It's getting a DPA signed. A known process, with known owners — not a verdict on anyone's trustworthiness.
If you want help navigating the tactical details of procurement, I'm here. But honestly? You don't need me for that. You already know who needs to sign where.
Where I can actually help is earlier. Through discovery, I'll help you run the bake-off for what tools fit your org — and shine a light on the value that's quietly slipping by, so this generational shift gets the attention it deserves instead of dying in a procurement queue.


Let’s Turn Your Data into Growth
No more guesswork or missed opportunities.


